On 20 February 2027 the transition period for NEN 7510 ends. From that day, only certificates issued against NEN 7510:2024 remain valid; a certificate on the 2017 version no longer counts. Today, 8 October 2026, that leaves just over four months. Anyone who has not yet scheduled the transition audit has very little room left.
Earlier this year, our transition guide described the full journey in seven steps. This article is meant for the final phase: a checklist that shows you at a glance what is still open, and what to do about it in the months that remain.
Why the deadline is a hard one
NEN 7510 is the Dutch standard for information security in healthcare, published by NEN, the Royal Netherlands Standardization Institute. With the publication of the certification scheme NCS 7510:2025 on 20 February 2025, a two-year transition period began. Every certificate holder must complete a transition audit with its certification body within that period. That is where the practical problem lies: certification bodies have limited audit capacity and always see a peak in the final months before such a deadline. They therefore advise scheduling the transition audit well in advance. An organisation that still has to start realistically needs six to twelve months. Anyone starting today will have to make sharp choices.
The content is not a minor update either. NEN 7510-1:2024 and NEN 7510-2:2024 replace the 2017 version and follow the structure of ISO/IEC 27001:2022 and ISO/IEC 27002:2022: four themes (organisational, people, physical and technological) and 93 controls, supplemented with healthcare-specific measures. Your entire control framework is therefore reorganised.
The checklist for the final phase
Work through the seven points below. Every point you cannot answer with "yes, and the evidence is ready" deserves an owner and a date this month.
1. Has the transition audit been scheduled?
This is the first item, not the last. Contact your certification body today, ask which audit dates are still available and which documents they want to receive in advance. Some certification bodies apply their own cut-off dates that fall before 20 February 2027. Confirm the appointment and plan backwards from that date.
2. Has the gap analysis been completed?
The gap analysis shows which requirements of the 2024 version are already covered by existing controls and where additions are needed. If this analysis is older than six months, or was never formally completed, do it again. Without a current gap analysis you do not know how much work remains.
3. Is the Statement of Applicability in the new structure?
The Statement of Applicability (SoA) has been renumbered to the layout of ISO/IEC 27002:2022. An SoA that still uses the 2017 clause numbers is an immediate finding for the auditor. Check for each control whether it applies, whether the justification is correct and whether the reference to the measure is current. Do not forget the healthcare-specific additions.
4. Have the new controls been implemented, with evidence?
The 2022 structure introduces new controls that did not exist in 2017. Go through them explicitly:
A sentence in a policy is not enough. For every control it must be demonstrable that the measure works: configurations, logs, test reports or exercise records. Pay particular attention to patient data, medical devices and the interfaces with supply-chain partners.
5. Have the internal audit and management review been carried out against the new standard?
The certification body expects you to have already assessed yourself against NEN 7510:2024. That means an internal audit on the new control structure and a management review in which the board has discussed the results, the residual risks and the updated risk assessment and context. Schedule both well before the transition audit, so that you have time left to resolve findings.
6. Have employees been informed and trained?
During the audit, auditors talk to employees on the work floor. They need to know what has changed and what it means for their work, from reporting incidents to handling patient data. Record who has completed which training; an attendance list or a record in your learning system is sufficient evidence.
7. Have suppliers and processors been checked?
NEN 7510:2024 places more emphasis on the supply chain. Check whether agreements with suppliers, processors and ICT partners cover the new requirements, whether their certificates are current and whether you have documented assessments of critical suppliers. A supplier without a valid certificate will soon be your problem too.
What if you do not make it?
If the transition period expires without a completed transition audit, your certificate loses its validity. In practice, that means a new certification process, with the associated costs and lead time. For healthcare organisations and their suppliers, demonstrability towards supply-chain partners, purchasers and regulators weighs heavily. If you notice that the schedule is becoming too tight, discuss it with your certification body now rather than hoping it will work out.
How uComply helps
The NEN 7510:2024 content pack in uComply contains all controls in the new structure, including the healthcare-specific measures. The transition mapping automatically links your existing controls to the new requirements, so the gap analysis immediately shows what is already covered and where work remains. The Statement of Applicability automatically follows the new layout, so there is no manual renumbering.
If you also work with ISO 27001:2022, you manage one set of controls linked to both standards. One measure, one evidence file, two ticks. You record the internal audit and the management review in the app, with findings, decisions and assigned actions that do not slip out of sight.
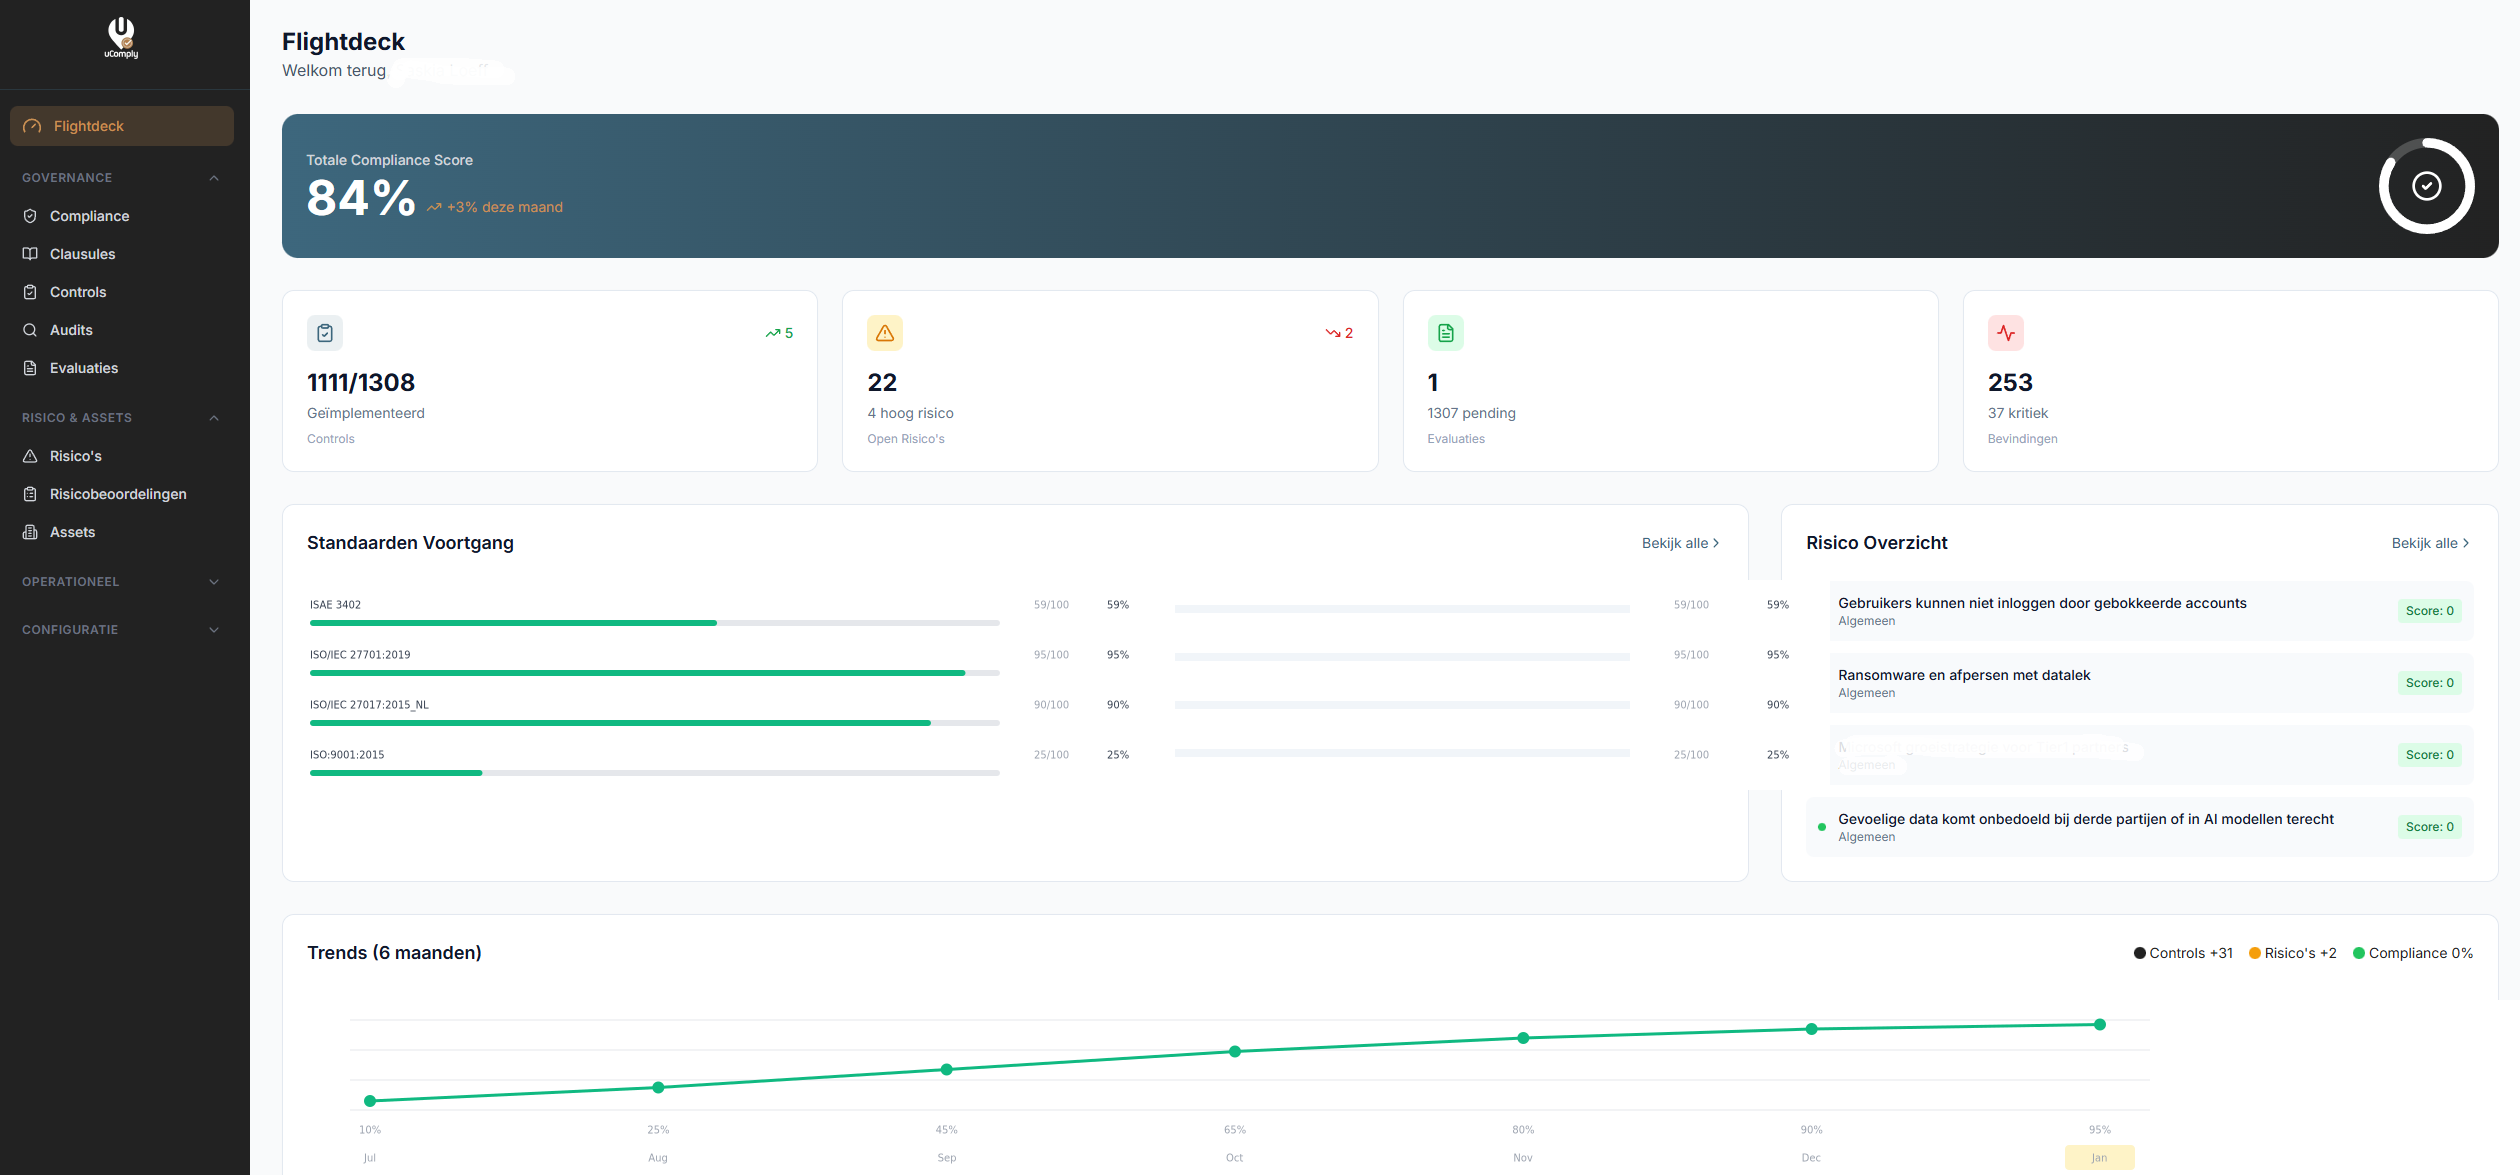
With Reminders you give every task in this checklist an owner and a deadline; uComply sends reminders in a building cadence, so nothing is left behind. In Flightdeck you see progress per standard, and therefore exactly how far you still are from 20 February 2027.
Summary
Just over four months is enough, but only if the transition audit is scheduled today and the seven points above each have an owner. Plan backwards from the audit date, focus on evidence rather than policy, and involve suppliers in time. Would you like to see how uComply keeps the final phase of your NEN 7510 transition under control? Book a no-obligation demo or view our pricing.
Sources
More on NEN 7510? Our standard page on NEN 7510 certification in healthcare brings together the requirements, the audit, a checklist and the difference with ISO 27001.